

Document Owner/文件负责人:
Rockchip Product Security Incident Response Team (PSIRT) / Rockchip 产品安全事件响应团队 (PSIRT)
Version /版本: V1.1.0
Published Date/发布日期: 2026/8/17
Public Location /公开位置:
https://www.rock-chips.com/a/en/psirt
https://www.rock-chips.com/.well-known/security.txt
Classification /密级: Public /公开
1. Scope of Responsibilities / 职责范围
Rockchip Product Security Incident Response Team (PSIRT) is responsible for receiving, investigating, and disclosing the security vulnerability information related to Rockchip products and solutions. We encourage that professional researchers, organizations, government agencies, and vendors report relevant security vulnerabilities to Rockchip PSIRT
Rockchip 产品安全事件响应团队(PSIRT)负责接收、调查和披露与 Rockchip 产品及解决方案相关的安全漏洞信息。我们鼓励专业研究人员、组织、政府机构和供应商及时向 Rockchip PSIRT 报告相关安全漏洞。
Policy scope / 策略适用范围
· Security incidents in hardware or software of Rockchip products / Rockchip 产品软硬件中的安全事件
· Defects in safety information or recommendations in Rockchip documents, e.g., datasheets and application notes / Rockchip 文档中的安全信息或建议缺陷(如数据手册、应用笔记)
· Security-sensitive documents or security-related information found in places where they should not be provided / 在不应提供的场所发现的安全敏感文档或安全相关信息
· Security-sensitive Rockchip products found in places where they should not be provided / 在不应提供的场所发现的安全敏感 Rockchip 产品
Out of scope / 范围外内容
· Vulnerabilities in Rockchip IT systems, such as the website. Still, you can send the relevant information to PSIRT, which will be forwarded to the appropriate Rockchip teams. / Rockchip IT 系统中的漏洞(如网站)。仍可将相关信息发送给 PSIRT,我们会转交给相应团队。
· Any other supports or events. E-mails regarding product support and other unrelated topics will not be responded by PSIRT. / 任何其他支持或事件。关于产品支持及无关主题的邮件,PSIRT 不予回复。
· Third-party services we do not operate / 我们不运营的第三方服务
· Findings that are already public / 已公开的发现
· Reports with no demonstrable security impact / 无法证明有安全影响的报告
· Volumetric denial-of-service testing / 大流量拒绝服务测试
· Social engineering of our staff or customers / 针对我们员工或客户的社会工程攻击
2. Process / 流程
Rockchip PSIRT Process / Rockchip PSIRT 流程
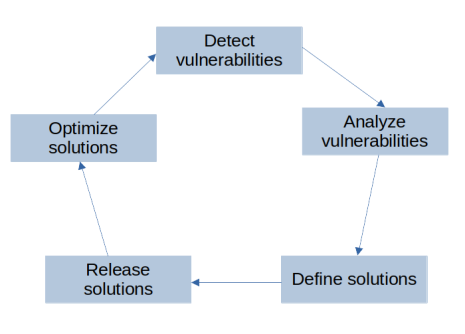
a) Detect vulnerabilities / 发现漏洞
To timely process security vulnerabilities, we must detect them in the first place. On the one hand, Rockchip encourages security researchers, organizations, customers, and vendors to report potential vulnerabilities to Rockchip PSIRT in a timely manner. On the other hand, Rockchip keeps monitoring well-known public vulnerability repositories, open-source communities, and security websites to detect vulnerabilities related to Rockchip products. When a potential vulnerability is reported to Rockchip PSIRT, PSIRT confirms the receipt of the report and notifies the appropriate technical team to analyze the vulnerability.
为及时处理安全漏洞,首先必须发现它们。一方面,Rockchip 鼓励安全研究人员、组织、客户和供应商及时向 Rockchip PSIRT 报告潜在漏洞;另一方面,Rockchip 持续监控知名公开漏洞库、开源社区和安全网站,以发现与 Rockchip 产品相关的漏洞。当潜在漏洞报告给 Rockchip PSIRT 时,PSIRT 确认收到报告并通知相应技术团队进行分析。
b) Analyze vulnerabilities / 分析漏洞
For any potential vulnerabilities reported to Rockchip PSIRT, the technical team analyzes them as soon as possible and confirm the validity and influence of the vulnerabilities; Rockchip uses the most popular Common Vulnerability Scoring System (CVSS) to analyze the severity of vulnerabilities.
针对报告给 Rockchip PSIRT 的任何潜在漏洞,技术团队会尽快分析,确认其有效性和影响范围;Rockchip 采用通用漏洞评分系统 (CVSS) 评估漏洞严重程度。
c) Define solutions / 确定解决方案
Vulnerability severity levels are assessed based on the actual impact to determine the priorities according to which solutions are provided. Rockchip develops patches or updates software versions for the affected products, and conduct sufficient tests to ensure the effectiveness.
基于实际影响评估漏洞严重等级,以确定解决方案优先级。Rockchip 为受影响产品开发补丁或更新软件版本,并进行充分测试以确保有效性。
d) Release solutions / 发布解决方案
Rockchip releases the patches or software versions to customers, and notifies customers in the Security Advisory (SA) or software release notes, so that customers make risk policies accordingly.
Rockchip 向客户发布补丁或软件版本,并通过安全公告 (SA) 或软件发布说明通知客户,以便客户制定相应风险策略。
e) Optimize solutions / 优化解决方案
Rockchip collects feedbacks from customers and optimizes the solutions when necessary. We will also continue to improve the vulnerability handling process.
Rockchip 收集客户反馈,在必要时优化解决方案。我们也将持续改进漏洞处理流程。
3. How to Report / 如何报告
Potential security vulnerabilities can be reported by email: [psirt@rock-chips.com](mailto:psirt@rock-chips.com), or by telephone with 400-7700-590 for China mainland, 0086-591-83991906 Ext:8198 for oversea.
国外请拨打:0086-591-83991906,转8198
可通过电子邮件报告潜在安全漏洞:[psirt@rock-chips.com](mailto:psirt@rock-chips.com) 或 全国统一客服热线:400-7700-590,国外请拨打:0086-591-83991906,转8198。
Since vulnerability information is relatively sensitive, we strongly recommend that you use our [PGP Key](https://www.rock-chips.com/uploads/240514/Rockchip_PSIRT_0xB12ADB4F_public.asc) when reporting security vulnerabilities to Rockchip PSIRT.
由于漏洞信息较为敏感,我们强烈建议在向 Rockchip PSIRT 报告安全漏洞时使用我们的 [PGP 密钥](https://www.rock-chips.com/uploads/240514/Rockchip_PSIRT_0xB12ADB4F_public.asc)。
Secure and anonymous reporting / 安全与匿名报告
To protect sensitive vulnerability information while it is being exchanged: / 为在交换过程中保护敏感的漏洞信息:
Our web form is served over HTTPS. / 我们的网页表单通过 HTTPS 提供。
You may encrypt email to us using our PGP key (fingerprint: 55B7 E7AE E8B8 D1DB 1ED2 7EB2 E180 A02D B12A DB4F), available from https://www.rock-chips.com/uploads/240514/Rockchip_PSIRT_0xB12ADB4F_public.asc. / 您可使用我们的 PGP 密钥(指纹:55B7 E7AE E8B8 D1DB 1ED2 7EB2 E180 A02D B12A DB4F)对发给我们的邮件加密,公钥可从 https://www.rock-chips.com/uploads/240514/Rockchip_PSIRT_0xB12ADB4F_public.asc 获取。
You may report anonymously. If you would like a response, please give us a contact address or an alias. / 您可以匿名报告。若希望得到回复,请提供联系地址或别名。
We will still accept reports sent through less secure channels — please do not let the lack of encryption stop you from reporting. / 我们仍会接受通过较不安全渠道发送的报告——请不要因缺少加密而放弃报告。
What to include in your report / 报告中应包含的内容
To help us validate and fix the issue quickly, please include as much of the following as you can: / 为帮助我们快速验证和修复问题,请尽可能包含以下内容:
Product identification — the affected product or service name, the affected version(s), and the platform or environment (OS, hardware) where applicable. / 产品标识——受影响的产品或服务名称、受影响版本,以及适用时的平台或环境(操作系统、硬件)。
Vulnerability description — what the issue is and where it exists, and its type or class (e.g., buffer overflow, SQL injection, improper authentication). / 漏洞描述——问题是什么、存在于何处,及其类型或类别(如缓冲区溢出、SQL 注入、不当鉴权)。
Impact — the potential impact if the issue is exploited (confidentiality, integrity or availability), and a severity assessment or CVSS score if you have one. / 影响——问题被利用时的潜在影响(机密性、完整性或可用性),以及严重性评估或 CVSS 评分(如有)。
Reproduction steps — step-by-step instructions to reproduce the issue, and proof-of-concept code or technical evidence if available. / 复现步骤——复现该问题的分步说明,以及概念验证代码或技术证据(如有)。
Discovery information — the date you found the issue and how (testing method, tool, or accidental finding). / 发现信息——您发现问题的日期及方式(测试方法、工具或偶然发现)。
Your contact information — your name or alias (you may remain anonymous) and a channel for follow-up. / 您的联系信息——您的姓名或别名(可匿名)以及用于后续跟进的渠道。
Disclosure intent — whether you intend to publish your findings, and any date you are working toward. / 披露意向——您是否打算公开发现,以及您争取的任何日期。
4. Policies /策略
We are committed to providing safe, reliable, and innovative products for customers. In order to maximize the efficiency of analyzing, resolving, and disclosing security vulnerabilities, we urge you to comply with the following policies when you submit vulnerability reports.
我们致力于为客户提供安全、可靠、创新的产品。为最大化分析、解决和披露安全漏洞的效率,提交漏洞报告时请遵守以下策略。
Disclosure Policies / 披露策略
Security vulnerabilities must be related to defects in hardware or software of Rockchip products or in Rockchip documents regarding security information or recommendations (e.g., datasheets and application notes). /安全漏洞必须与 Rockchip 产品的软硬件缺陷,或 Rockchip 文档中的安全信息/建议缺陷(如数据手册、应用笔记)相关。
Security issues are yet unknown to Rockchip and are only reported to Rockchip. /安全问题尚未为 Rockchip 所知,且仅向 Rockchip 报告。
All security information must be kept confidential before being disclosed. Limit access to non-public vulnerability information in accordance with the "need-to-know" principle./ 所有安全信息在披露前必须保密。根据“知情必要”原则来限制对非公开漏洞信息的访问。
Invasion of privacy, disruption of the product ecology, and destruction or tampering of data are not allowed. /不得侵犯隐私、破坏产品生态、销毁或篡改数据。
When different persons submit the same security issue, only the first one is listed in our security acknowledgement. /多人提交同一安全问题时,仅首位报告者列入安全致谢。
Security vulnerability submissions may be additionally restricted by applicable laws. /安全漏洞提交可能受适用法律额外限制。
Your tests should not violate any laws, nor destroy or affect any data that does not belong to you. This policy is consistent with the general vulnerability disclosure practices. Any activities that violate laws or may result in the breach of legal obligations are not allowed. / 您的测试不得违反法律,不得销毁或影响非您所有的数据。本策略与通用漏洞披露实践一致。任何违法或可能导致违反法律义务的活动均不允许。
Rockchip reserves the right to determine the eligibility of submissions. / Rockchip 保留决定提交资格的权利。
What you can expect from us / 您可期待我们做到
After you submit a report, we will: / 提交报告后,我们将:
acknowledge receipt within 3 business days and assign a tracking reference; / 3 个工作日内确认收到并分配跟踪编号(格式:RKVUL-YYYY-XXXXXX);
aim to triage and validate your report within 14 business days, and contact you if we need more information; / 14 个工作日内完成分级与验证,如需更多信息将与您联系;
keep you informed of our progress at reasonable intervals (at least every 14 days); / 以合理间隔(至少每 14 天)通报进展;
aim to deliver a resolution within 90 calendar days, depending on complexity and any third parties involved; / 90 个自然日内交付解决方案,视复杂度及所涉第三方而定可调整;
notify you when the vulnerability has been remediated, and may invite you to confirm that the fix resolves it. / 修复发布时通知您,并可能邀请您确认修复是否解决问题。
Coordinated disclosure /协调披露
We follow a coordinated disclosure approach: /我们遵循协调披露原则:
We ask that you give us a reasonable opportunity to remediate the issue before disclosing it publicly. / 请您在公开披露前给予我们合理的修复机会。
We will not publicly disclose details of a reported vulnerability before it has been addressed; any public disclosure will be coordinated and agreed between you and us. / 漏洞处理前不公开细节;任何公开披露将由双方协调并达成一致。
Where appropriate we agree an embargo period. Embargo timelines can be adjusted case by case by mutual agreement, including where a coordinator or other vendors are involved. / 适当情况下约定禁披期。禁披时限可经双方同意逐案调整,包括涉及协调者或其他供应商时。
When a fix is released, we publish a security advisory and, where appropriate, request a CVE identifier as an international standard identifier. / 修复发布时,我们将发布安全公告,并在适当情况下申请 CVE 编号(作为国际标准标识)。
Where to find our security advisories / 安全公告发布渠道
When a vulnerability has been remediated, we publish a security advisory so that users can assess whether they are affected and how to update. You can find our advisories at: / 漏洞修复后我们将发布安全公告,以便用户评估影响及更新方式。公告发布于:
Security advisory page: https://www.rock-chips.com/a/en/psirt/advisories. / 安全公告页面:https://www.rock-chips.com/a/en/psirt/advisories。
Confidentiality and recognition /保密与致谢
We treat vulnerability reports as confidential. We will not share the personal information you provide with third parties without your explicit consent, except where required by law. / 我们将漏洞报告视为机密。未经您明确同意,不与第三方共享您提供的个人信息(法律要求除外)。
With your permission, we are happy to credit you for your discovery in our advisory or on our acknowledgements page. Let us know if you would prefer to remain anonymous. / 经您许可,我们乐于在公告或致谢页面为您署名。若您希望匿名,请告知我们。
Safe harbour and good-faith research /安全港与善意研究
If you make a good-faith effort to comply with this policy during your research, we will consider your research authorized, we will work with you to understand and resolve the issue quickly, and we will not pursue or support legal action against you. / 若您在研究过程中善意遵守本策略,我们将视您的研究为已授权,与您合作快速理解和解决问题,不对您提起或支持法律诉讼。
Good-faith research means, among other things, that you: /善意研究尤其意味着您:
only interact with systems or accounts you own or have explicit permission to test; / 仅与您拥有或获明确许可测试的系统或账户交互;
avoid privacy violations, destruction of data, and any degradation of our services (for example, no denial-of-service testing); / 避免侵犯隐私、销毁数据、降低服务质量(如不进行拒绝服务测试);
access only the minimum data necessary to demonstrate the issue, and do not store, share or use it; / 仅访问证明问题所需的最少数据,不存储、共享或使用该数据;
Rockchip Electronics Co., Ltd. All rights reserved
闽ICP备19006074号-1  闽公网安备 35010202001061号